

October 17, 2026/
SOC 2 readiness activities may include policies, risk assessments, controls, evidence collection, employee training and monitoring activities. Companies may therefore...
SOC 2 readiness activities may include policies, risk assessments, controls, evidence collection, employee training and monitoring activities. Companies may therefore...
A SOC 1 examination can offer an independent evaluation of certain controls for an organization whose services have an impact...
SOC 1 attestation can assist service organizations in demonstrating the effectiveness of controls relevant to their customers’ internal control...
SOC 2 compliance matters more than ever for companies in tech, whether they’re offering software, cloud services, or processing...
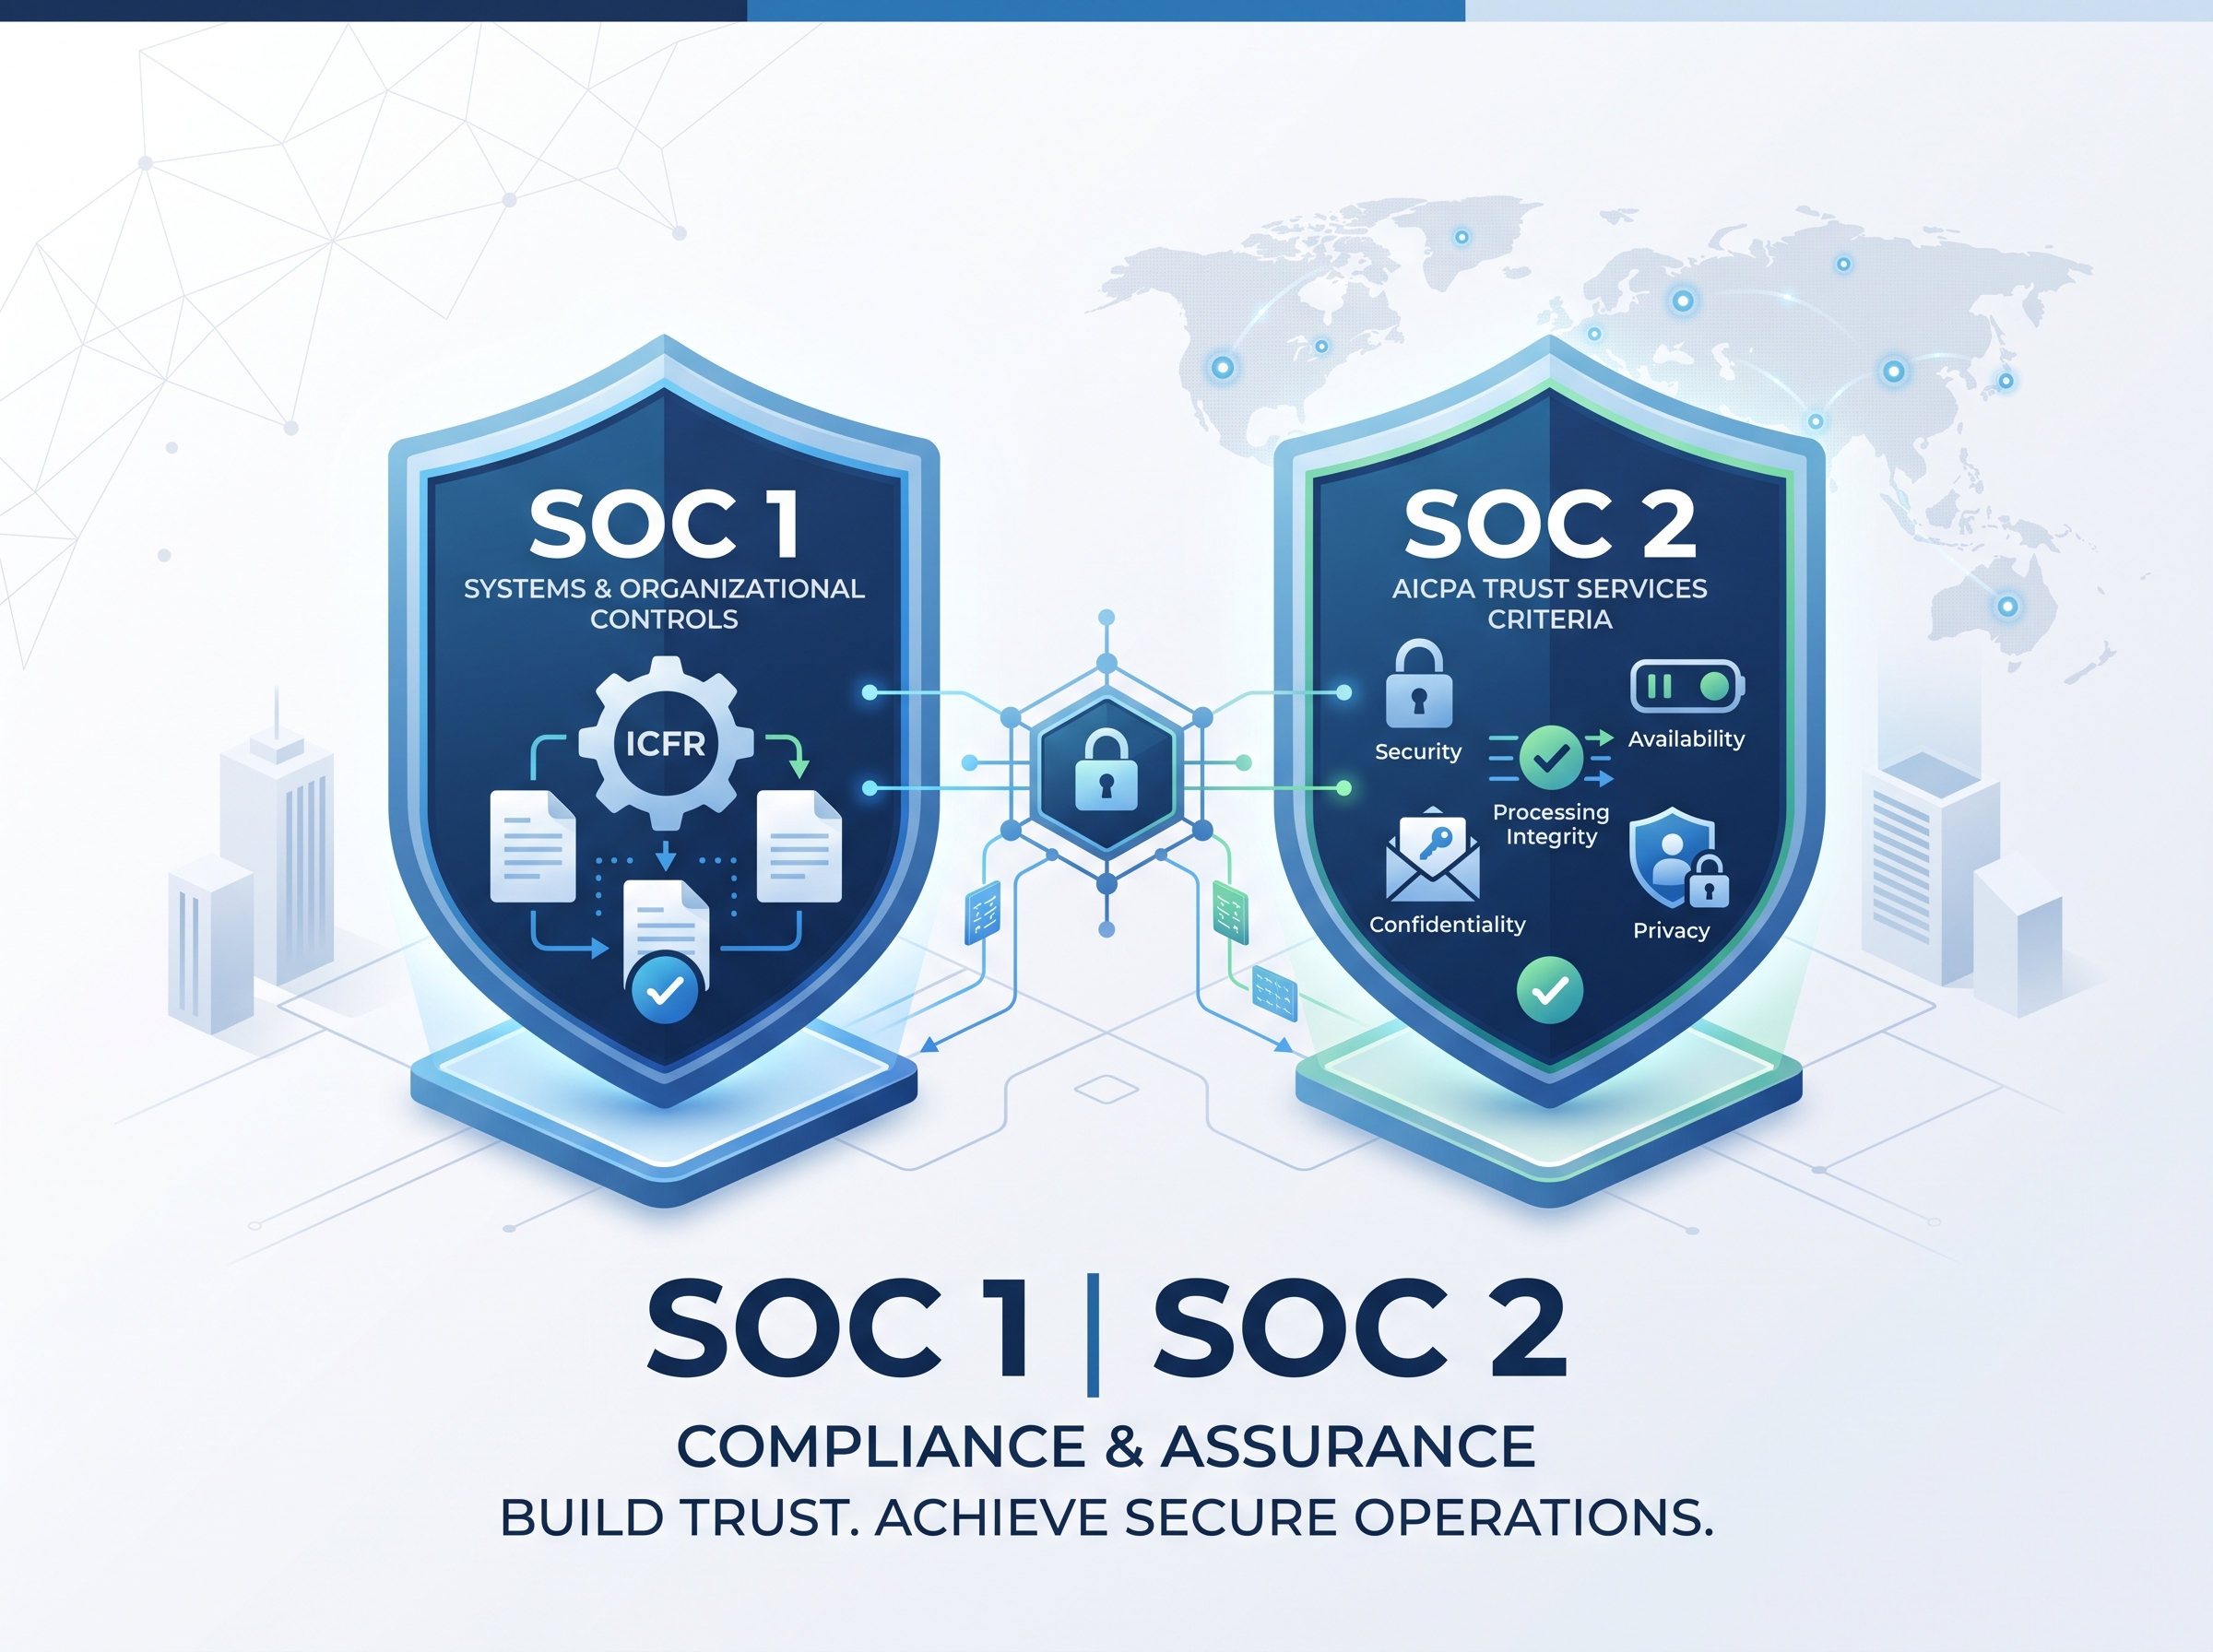
SOC compliance is essential to meet security expectations. Nevertheless, attaining and sustaining compliance with these standards can prove to...
Vulnerability Assessment and Penetration Testing or VAPT testing is one of the best practices that help in detecting, assessing,...
As businesses switch to digital platforms, cloud infrastructure, and data-driven operations, customers demand strong security measures to protect their...
Today, cyber threats have become more frequent than ever before. US businesses face constant risks from ransomware, phishing attacks,...
In today’s digital business environment, protecting sensitive information is more important than ever. Organizations that handle customer data, financial...
In today’s interconnected business environment, cyber threats are becoming more sophisticated and frequent. Organizations of all sizes face risks...
